

Since we now live in a digital world, it’s easy to commit a cybercrime. Statistics show that 2,244 cybercrimes are committed every single day.
Social engineering is a technique used by scammers and hackers to trick their targets into divulging personal information by appealing to their emotions. Those who fall victim to these data breaches may lose a great deal of money.
This article will discuss the various forms of social engineering and provide advice on how to avoid becoming a victim.
How forex trading accounts are hacked
1. Phishing
Criminals use phishing, also known as “spoofing,” to trick users into giving up sensitive information by making it appear as though the sender is from a trusted source.
Typically, victims are duped into divulging personal information, such as passwords and banking details, by receiving emails that appear to have come from a legitimate source but actually originate from a malicious domain.
2. Keylogging
The practice of secretly recording keyboard input is known as keylogging. Scammers frequently use a keylogger tool, either a computer program or a hardware device, to record the user’s keystrokes for later illegal use. Phishing attacks and remote downloads are common ways for hackers to install software keyloggers on your device without your knowledge. Some software keyloggers can also record what is copied to the clipboard and save screenshots of your computer’s screen. Antivirus programs can identify and eliminate these keyloggers. When a hardware keylogger is built into or attached to your device, it can be difficult to detect. In contrast to software keyloggers, these keyloggers would go undetected by antivirus programs.
3. Man-in-the-middle attack
The convenience of free public WiFi in every location comes with potential downsides. Man-in-the-middle (MitM) attacks can happen on public WiFi networks.
A man in the middle (MitM) attack occurs when a hacker poses as a trusted intermediary in order to steal sensitive information. A malicious third party could potentially hijack a user’s browser and direct them to a fraudulent website whenever they try to access a legitimate one.
4. Scareware
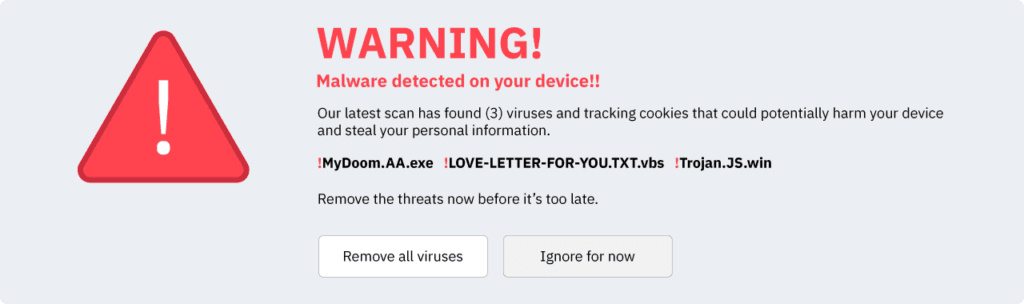
Scareware is malicious software designed to frighten its targets. Scammers use fake warnings to scare victims into downloading malware or visiting compromised websites.
An alarmist message like this one:
5. Baiting
How often do you get emails promising delivery of purchases you never made? If so, a con artist may have been trying to catch you off guard. Con artists who employ this strategy rely on their victims’ natural tendencies toward curiosity or greed.
If a website asks you to create an account before allowing you to download anything (ebooks, music, or movies), you should be wary. The information you provide is gold to con artists. Malware can be hidden in downloaded files and used to steal sensitive information.
Physical forms of baiting are also possible. Keep moving if you come across an unattended USB device or external hard drive. Con artists spread malware by leaving infected devices lying around, hoping that unsuspecting victims will plug them in and let the infection spread.
How to protect your forex trading account
1. For starters, you shouldn’t click on random links.
Always check to see that the URL starts with “HTTPS” rather than “HTTP,” and pay close attention to any spelling mistakes or strange characters it may contain. Do not enter your personal information on any website that does not start with HTTPS, or that uses an incorrect spelling of the word “Deriv,” which is our official website.
If you get an email that appears to be from a reputable company but asks you to verify your account information on a different website, you should not click on the link provided. Don’t follow any links that take you elsewhere on the Internet.